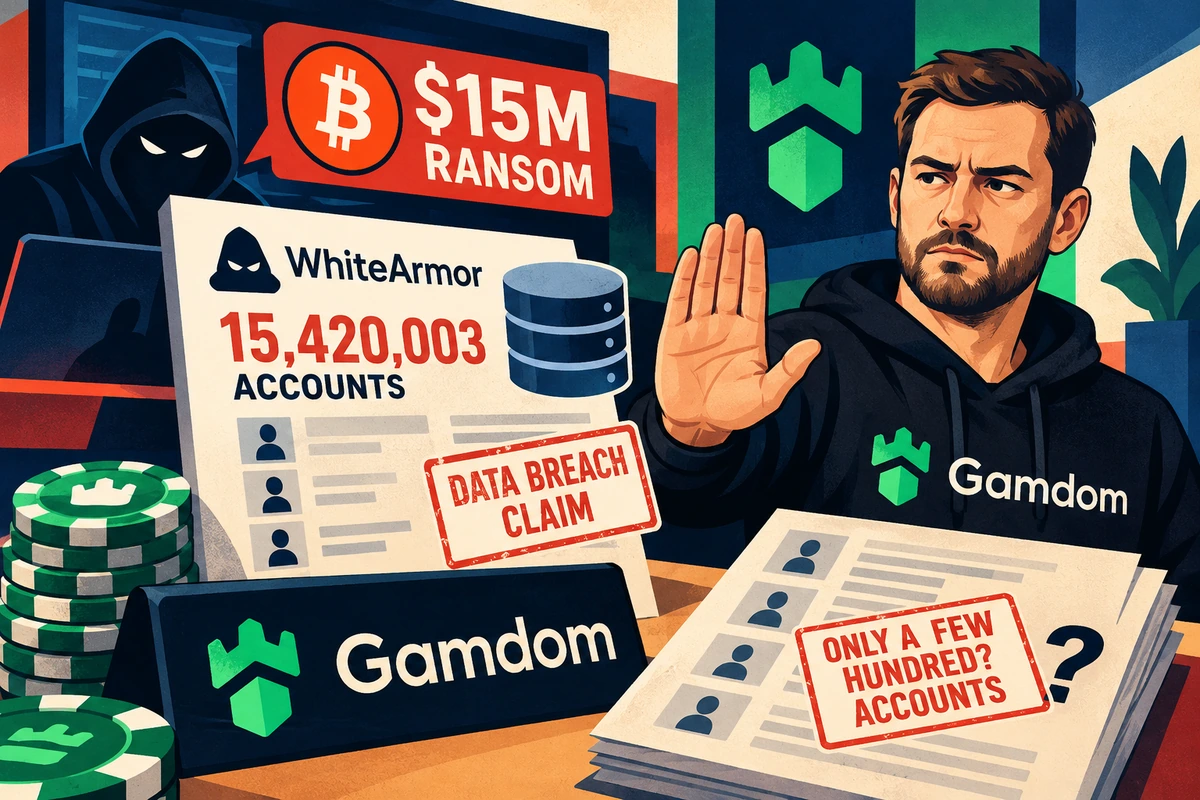

Cyber-extortion group WhiteArmor claims it obtained Gamdom’s full user database and is demanding $15 million in Bitcoin not to publish it. Gamdom founder Felix Römer disputes the headline figure of 15.4 million accounts, saying any genuine exposure may be limited to a few hundred records rather than a full database extraction.
WhiteArmor listed Gamdom on its leak site on October 26, 2026. Independent ransomware trackers recorded the listing, but the attackers’ claims about the amount and authenticity of the data have not been independently established.
The group says it holds records for 15,420,003 accounts across 146 database fields. It also released a sample containing about 100 records as purported proof and claimed that the accounts represented more than $1 billion in combined profit value. That valuation has not been substantiated.
For players, the important distinction is simple: the leak-site post is real, but a 15.4 million-account breach is not yet a verified fact.
Römer says the database claim is overstated
Bitcoin.com News reports that Römer initially disputed claims of widespread data extraction and suggested the attackers possessed only a few hundred accounts. Later statements acknowledged possible exposure of usernames, email addresses and gambling activity, while maintaining that identity-verification documents were unaffected.
WhiteArmor says its access came through an old internal machine account that still retained administrative privileges because its credentials had not been rotated. That remains the attackers’ account of the intrusion; Gamdom has not publicly confirmed that access path.
The earlier attack already cost Gamdom millions
The extortion claim follows a confirmed breach on October 13. During that incident, Gamdom took its systems offline after discovering an unauthorized connection on an automation server.
Römer said the hot-wallet drain cost just over $3 million. Independent on-chain analysis placed the total around $4.2 million across several networks.
Gamdom returned online on October 16. The company has said player balances were safe, but it has not published a full forensic post-mortem that independently resolves the attack path or the scope of any account-data exposure.
What Gamdom users should do now
The uncertainty over scale does not make the data-risk claim irrelevant. Even a much smaller set of exposed account records could be used for targeted phishing, credential stuffing or impersonation attempts.
Players who reused the same password elsewhere should change it on those other services and use unique passwords going forward. Multi-factor authentication should be enabled wherever available. Users should also treat unexpected messages about Gamdom refunds, account verification, password resets or compensation as potential phishing attempts and avoid opening files advertised as leaked samples.
There is currently no public evidence that Gamdom paid WhiteArmor’s ransom, and no independent confirmation that the group possesses 15.4 million genuine account records.
Email support@casinocomplaints.org with the article link and source. Editorial process →︎
Sources & checks
- Cyber Threat Intelligence: Gamdom — Whitearmor ransomware victim recordcyberthreatintelligence.net · Checked 28 Oct 2026
- Bitcoin.com News: Gamdom faces $15M bitcoin ransomnews.bitcoin.com · Checked 28 Oct 2026
- TokenPost: Whitearmor’s Gamdom ransom claimtokenpost.com · Checked 28 Oct 2026
- Bitcoin.com News: Gamdom goes dark after $3 million wallet hacknews.bitcoin.com · Checked 28 Oct 2026
- Nexus Mutual: Onchain Security Roundup, Oct 12–18nexusmutual.io · Checked 28 Oct 2026
Article updates1
Published from the news package.