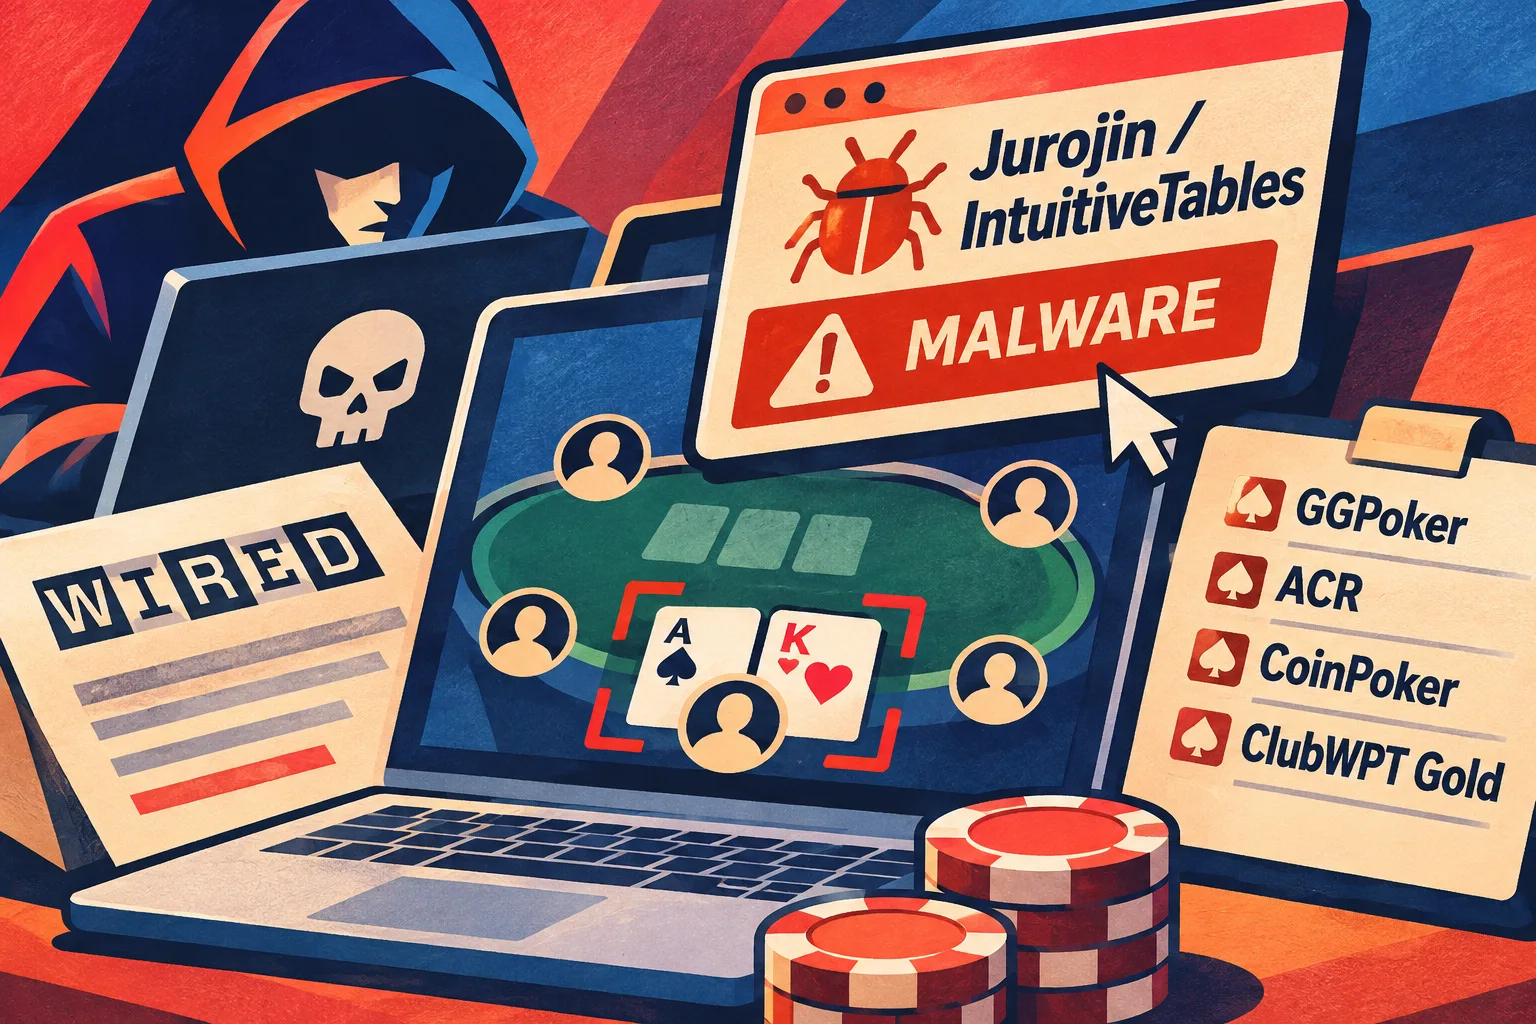

A targeted malware operation delivered through two popular multi-tabling tools gave an accused cheater remote access to selected high-stakes poker players’ computers, allowing their hole cards to be viewed during online games. WIRED reported on 29 October 2026 that the suspected player remained active on GGPoker and ACR until late September, with sources estimating losses of $1.5 million to $4 million on those two sites.
The scheme became public on 29 September, when cybersecurity consultant WolfSec disclosed the MeshAgent compromise. WIRED’s investigation added how the malware reached players, how narrowly parts of it were activated and how different poker rooms responded. WIRED did not name the accused player, who has not been charged.
Compromised poker tools delivered the remote-access software
According to WIRED, the attacker compromised Jurojin and IntuitiveTables, two programs used to manage multiple poker tables. WolfSec told the magazine the attacker pushed malicious software to an estimated more than 1,000 users. Alex, a professional player who spoke under a pseudonym, was described as one of hundreds of players allegedly targeted over several years.
In Jurojin’s case, the attacker gained access to the software’s update system and could send altered packages through the normal update channel. Jurojin’s own technical notice later dated the tampered uploads from 11 June 2025 through 28 January 2026. They were not one continuous infection: the company counted 92 separate windows in which a tampered zip was current, then replaced by a clean build. The last tampered file was replaced on 28 January 2026. Only accounts moved into a specific update group received the altered path.
The IntuitiveTables compromise followed a different path. WIRED reported that the developer’s test computer was infected through Jurojin, after which the attacker inserted malicious code into an IntuitiveTables build before it was digitally signed and published. WIRED said everyone who installed that build also installed a backdoor. The same account says the altered software checked a player’s poker username against a list on the attacker’s servers, and that only names on the list triggered additional malicious files, including MeshAgent. Players who were not on the list saw a program that otherwise behaved normally.
One player WIRED identified as Alex found MeshAgent on his computer on 25 September. It had been installed on 24 April. He found 11 apparent screen-capture events during ACR sessions, with the same opponent present in 10 of them, and estimated his own losses at about $30,000.
Poker rooms took different approaches to refunds
CoinPoker began investigating the suspicious player in 2025, banned the account and refunded more than $100,000 to affected players, according to Mario Mosböck, a CoinPoker ambassador authorised to speak about the response. He told WIRED the payout was delayed for several months because the alleged cheater appealed the confiscation to regulators.
ClubWPT Gold banned an account linked to the scheme after the malware became public and refunded a player who had lost money in a June 2026 heads-up session, its head of customer operations told WIRED.
GGPoker announced measures on 15 October, including a ban on third-party poker software and win-rate anomaly detection. The company said it traced the accused attacker’s funds to a Coinbase account, asked Coinbase to restrict the account and preserve its records, and gave wallet addresses to industry watchdogs and law enforcement. A player told WIRED he had reported the account in early September and was later told there had not been conclusive evidence to act at the time.
ACR took the opposite position. WIRED reported that an 18 October message to players said its security review found no compromised game outcomes or wrongdoing and that it would not issue refunds. The same communication introduced a feature designed to stop remote-viewing tools from capturing hole cards.
For players, the risk extends beyond a single poker account. MeshAgent is remote-administration software capable of viewing or controlling an infected computer. Anyone who used the affected tools during the relevant period should treat the device itself as potentially compromised, preserve hand histories and security logs, and not assume that a poker room will automatically reimburse disputed losses.
Email support@casinocomplaints.org with the article link and source. Editorial process →︎
Sources & checks
Article updates1
Published from the news package.